
GitHub Security Risk Assessments Now Indicate Repository Protection Status
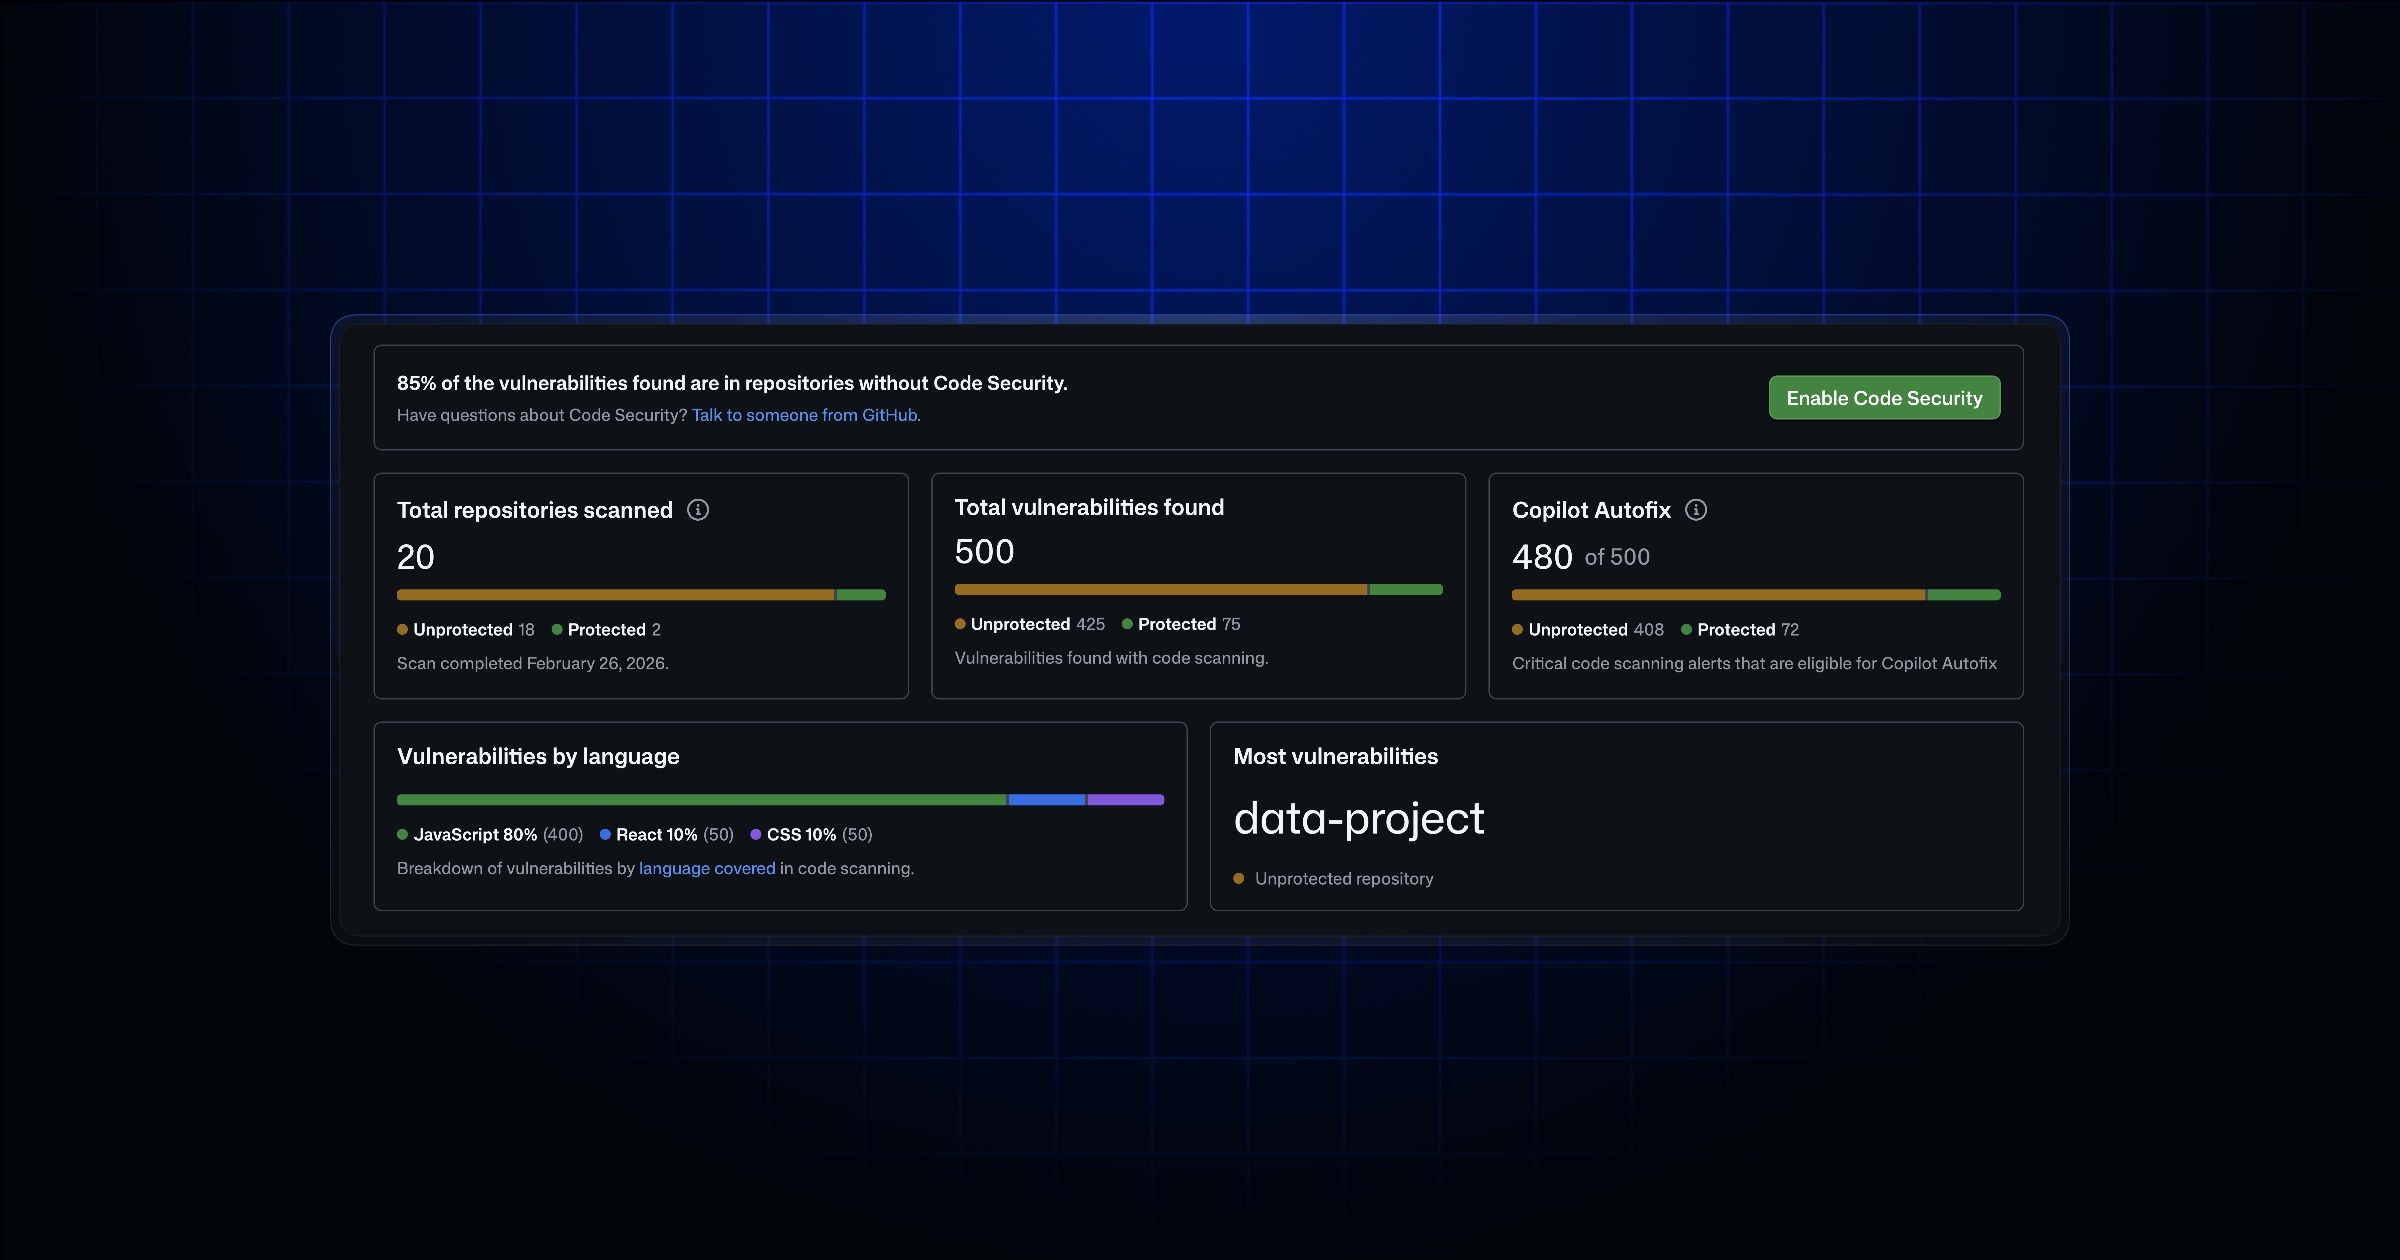
GitHub's code and secret risk assessments now display whether security findings are in protected or unprotected repositories, helping teams identify where additional security coverage may be needed.
What changed?
GitHub has updated its code security risk assessment and secret risk assessment tools to now identify whether security findings are in protected or unprotected repositories. This feature is immediately available for users of GitHub Enterprise Cloud and GitHub Team, and will be available for secret risk assessment users on GitHub Enterprise Server starting with version 3.24.
Why does it matter to an everyday developer?
With this update, developers and security managers can more quickly identify where security coverage may be insufficient, especially in unprotected repositories. Understanding the protection status of a repository streamlines risk prioritization, making it easier to address vulnerabilities in less protected environments and comply with organizational security policies.
What can the developer do now?
Developers using GitHub Enterprise Cloud or GitHub Team can review their code and secret risk assessments with the new repository protection status indicators. If findings are present in unprotected repositories, teams can take targeted actions such as enabling required branch protections or strengthening access controls. For Enterprise Server users, support for secret risk assessment protection status will begin with version 3.24.