
GitHub Agentic Autofix for Code Scanning Alerts Now Generally Available
GitHub has announced general availability of Agentic autofix for code scanning alerts on GitHub Enterprise Cloud. The tool, part of GitHub Code Security and Advanced Security suites, can now remediate alerts by exploring affected code, proposing fixes, validating them with CodeQL, and opening ready-to-review pull requests.
What changed?
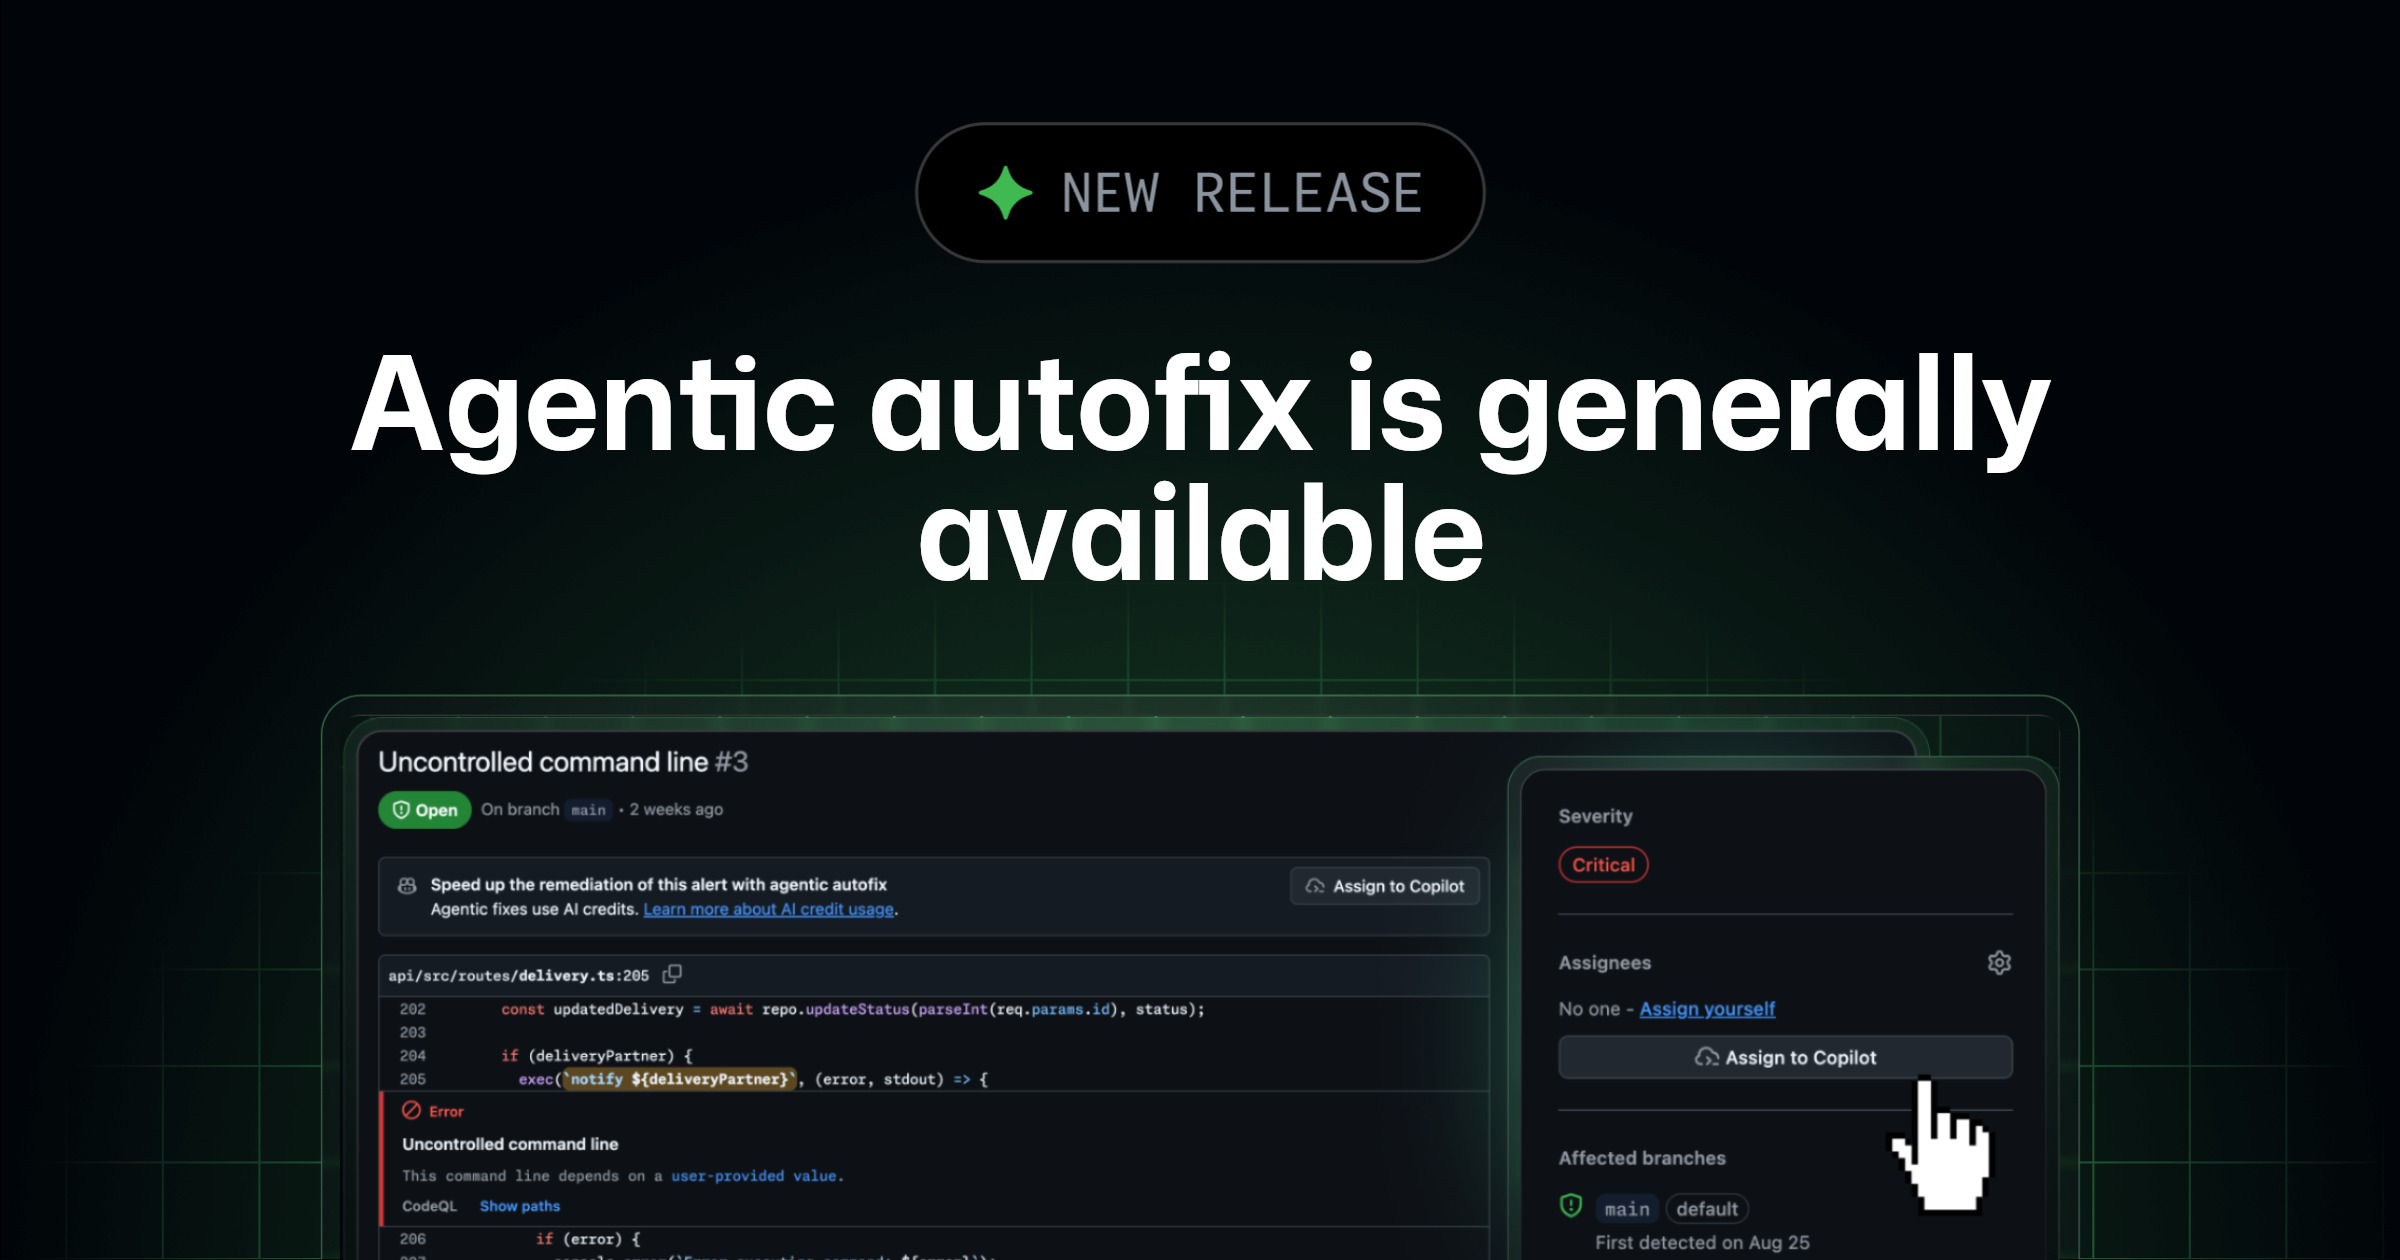
Agentic autofix for code scanning alerts is now generally available to GitHub Code Security and GitHub Advanced Security customers on GitHub Enterprise Cloud. The system remediates code scanning alerts by navigating relevant files, proposing a fix, re-running CodeQL to verify the fix resolves the original alert, and opening a draft pull request for human review. Users can assign up to 25 alerts at once for Copilot autofix, and direct further changes through comments or the Agents tab. The capability is only supported on the repository’s default branch. Access requires enabling a specific enterprise policy and an active Copilot billing method.
Why does it matter to an everyday developer?
Agentic autofix streamlines the process of handling security alerts detected by automated code scans. Developers no longer need to triage each security issue manually; instead, Copilot can propose and validate fixes, reducing remediation effort and supporting high-confidence, automated corrections. This can save time, especially when addressing multiple issues at once, and can lead to improved consistency and reliability of code fixes generated across the organization.
What can the developer do now?
- Request your enterprise administrator to enable the Agentic autofix policy in Advanced Security settings.
- Ensure your organization or repository has Copilot billing configured.
- Assign code scanning alerts on the default branch to Copilot using the GitHub UI or the Update a Code Scanning Alert REST API with assignees set to ["copilot-swe-agent[bot]"].